AI code audit for Claude Code, Copilot and Cursor
We check what your AI coding agents can read, run and send: files and secrets, shell commands, MCP servers and prompt injection paths. A focused audit for a team of up to 20 developers runs 1 to 2 weeks and ends with a written report of prioritized findings plus a hardened configuration package. For engineering leads rolling AI coding agents out across a team.
Free 30-min call. We name your top exposure points on the call, not behind a paid report.
Built for teams shipping AI to production. See the client list.
Teams we ship for


The new AI software engineering
Coding changed. Engineers stopped being the bottleneck.
The bottleneck moved to orchestration. Claude Code is the brain, MCP plugs into your stack, E2B sandboxes every action. One of our engineers ships like three normal hires.
- 01Claude Codethe brain · subagents · MCP
- 02Anthropicmanaged agents · runtime
- 03CursorIDE pair-programming
- 04n8ncron · webhooks · glue
- 05E2Bsandboxed compute
83%
of dev teams have no formal AI coding tool security policy
512K
lines of Claude Code source exposed in the 2026 npm leak, including hardcoded dev keys
1 in 3
AI-generated code snippets contains at least one security vulnerability
$4.88M
average cost of a data breach in 2026 (IBM Cost of Data Breach Report)
Why AI coding tools
become security liabilities
Claude Code and tools like it ship with permissive defaults built for a single developer. Rolled out across a team without hardening, those defaults create categories of risk most engineering leaders only discover after an incident.
Secret & Credential Exposure
AI coding agents read your entire codebase - including .env files, private keys, and database connection strings - and send that context to external inference APIs. Without explicit exclusion rules, your secrets leave your network with every prompt.
Prompt Injection via Malicious Files
An attacker who can place a file in your codebase can embed hidden instructions that Claude Code will execute when it reads that file. Third-party packages, client-submitted code, and public READMEs are all potential injection vectors.
Auto-Approval of Dangerous Actions
Claude Code's YOLO mode and MCP server integrations can execute shell commands, make network requests, and modify files without developer confirmation. One misconfigured permission scope in a production environment can cause irreversible damage.
What we check: four security pillars
The engagement covers every layer of your AI-assisted development workflow, from the initial audit through ongoing monitoring.
Need broader hands-on training on Cursor, MCP and agents for the whole team? See our AI workshops.
AI Tool Permission Audit
We map exactly what your AI coding agents can access: files, environment variables, shell commands, external APIs, and MCP server permissions. You get a complete picture of your attack surface before hardening begins.
- File system access scope and .claudeignore coverage
- Shell command allowlist and denylist rules
- MCP server inventory and OAuth token storage location
- Network egress rules and external API call permissions
Secure Configuration Setup
We configure .claudeignore to exclude sensitive files, set command allowlists, define approval gate policies, vet every MCP server, and integrate pre-tool hooks that validate actions before execution.
- CLAUDE.md and settings.json hardening
- Approval gates for destructive or production-touching commands
- Prompt injection guardrails on file and README ingestion
- PreToolUse and PostToolUse hook validation
Developer Security Training
A half-day workshop covering prompt injection recognition, context hygiene, safe .env practices, reviewing AI-generated code for vulnerabilities, and operating AI agents in production without creating liability.
- Recognizing prompt injection in files and pull requests
- Safe .env and credential handling around AI agents
- Reviewing AI-generated code for vulnerabilities before merge
- What to do if a tool call behaves unexpectedly
Ongoing Monitoring & Response
Monthly configuration audits as your codebase evolves, real-time alerting on policy violations, SAST pipeline maintenance, and an incident response playbook your team can execute without calling us first.
- Monthly configuration drift review
- Real-time alerting on policy violations
- SAST pipeline maintenance for AI-generated pull requests
- Incident response drill and playbook update
Known risk classes we check your setup against
These are publicly disclosed classes of Claude Code and MCP vulnerability, mapped to the OWASP Top 10 for Agentic Applications 2026 where it applies. The audit checks whether your configuration is exposed to each one.
Running agents beyond the IDE, on business systems or customer data? Walk through our AI agent production readiness checklist first, or have us build the agent with these controls in place through AI agent development.
Hook-based command injection
Lifecycle hooks that run shell commands automatically when a project opens are a documented remote code execution vector, tracked publicly as CVE-2025-59536. We check whether your hooks are scoped, reviewed, and cannot run unvetted commands on project open.
Environment variable exfiltration
Overriding a single environment variable can redirect authenticated API traffic to an attacker-controlled endpoint before any consent prompt appears, tracked publicly as CVE-2026-21852. We check your environment variable handling and outbound network rules for this pattern.
MCP OAuth token exposure
Some MCP integrations store OAuth tokens in plaintext configuration files on the developer machine. A compromised npm package or install script can read and exfiltrate that token without tripping an alert. We check where your MCP tokens live and how they are protected.
Prompt injection and goal hijacking
Ranked the top risk in the OWASP Top 10 for Agentic Applications 2026: content the agent reads, not the developer, changes what it does next. We check whether untrusted file content, comments, or third-party code can influence tool calls.
Agentic loop and sandbox escape
Agents that can modify their own execution environment have, in documented cases, disabled the sandbox meant to restrict them. We check whether your agent's tool calls are isolated from the host filesystem and network by default.
Supply chain and plugin risk
Malicious npm packages and unvetted MCP servers can rewrite local configuration files to redirect Claude Code's authenticated traffic to attacker infrastructure. We check your dependency and plugin install process for this exact pattern.
How It Works: Audit, Harden, Monitor
01
Audit
We review your current Claude Code and AI coding agent setup: file access scope, shell permissions, MCP servers, secrets exposure, and developer practices. You receive a written findings report with severity ratings.
- CLAUDE.md, settings.json, and hook configuration
- .claudeignore coverage and file access scope
- MCP server inventory and OAuth token storage
- Exposure to known CVEs and the OWASP Agentic Top 10
3-5 days
02
Harden
We implement the fixes: .claudeignore configuration, approval gates, MCP server scoping, hook policies, and CI/CD SAST integration. All changes are documented and version-controlled.
- .claudeignore rewrite and secrets exclusion
- Command allowlist and approval gate policy
- MCP server scoping and network isolation
- CI/CD SAST integration for AI-generated pull requests
5-7 days
03
Monitor
Monthly configuration reviews, developer training refreshers, and an on-call incident response SLA. As your team grows and your AI toolchain evolves, your security posture keeps pace.
- Monthly configuration drift review
- Real-time policy violation alerting
- Incident response playbook and drill
- Training refreshers as your team and toolchain grow
Ongoing retainer
Unsecured vs. AY Automate Secured
Default Claude Code installations are optimized for individual developer speed. Enterprise team deployments need a different posture.
What you get
Every engagement ends with working configurations your team can use on day one, plus the findings report behind them.
- Written security audit report with severity-rated findings
- Hardened .claudeignore configuration scoped to your codebase
- Shell command allowlist and approval gate policy
- MCP server trust register with per-server permission scopes
- SAST integration for AI-generated code in your CI/CD pipeline
- Developer security runbook (prompt injection, context hygiene, .env practices)
- Half-day team training workshop
- Incident response playbook
- Monthly monitoring retainer (optional)
Relevant if you are using
Claude Code (Anthropic)
Our primary focus area. We know the leaked architecture.
GitHub Copilot
Permission scoping and enterprise policy configuration.
Cursor
Rules files, .cursorignore, and context window hygiene.
MCP Servers
Trust assessment and permission scoping for any MCP integration.
Custom AI coding agents
Architecture review for internally built coding assistants.
Don't take it from us
Hear it from the operators we shipped for.
Real founders. Real cameras. No scripts. Different scales, same agent stack.
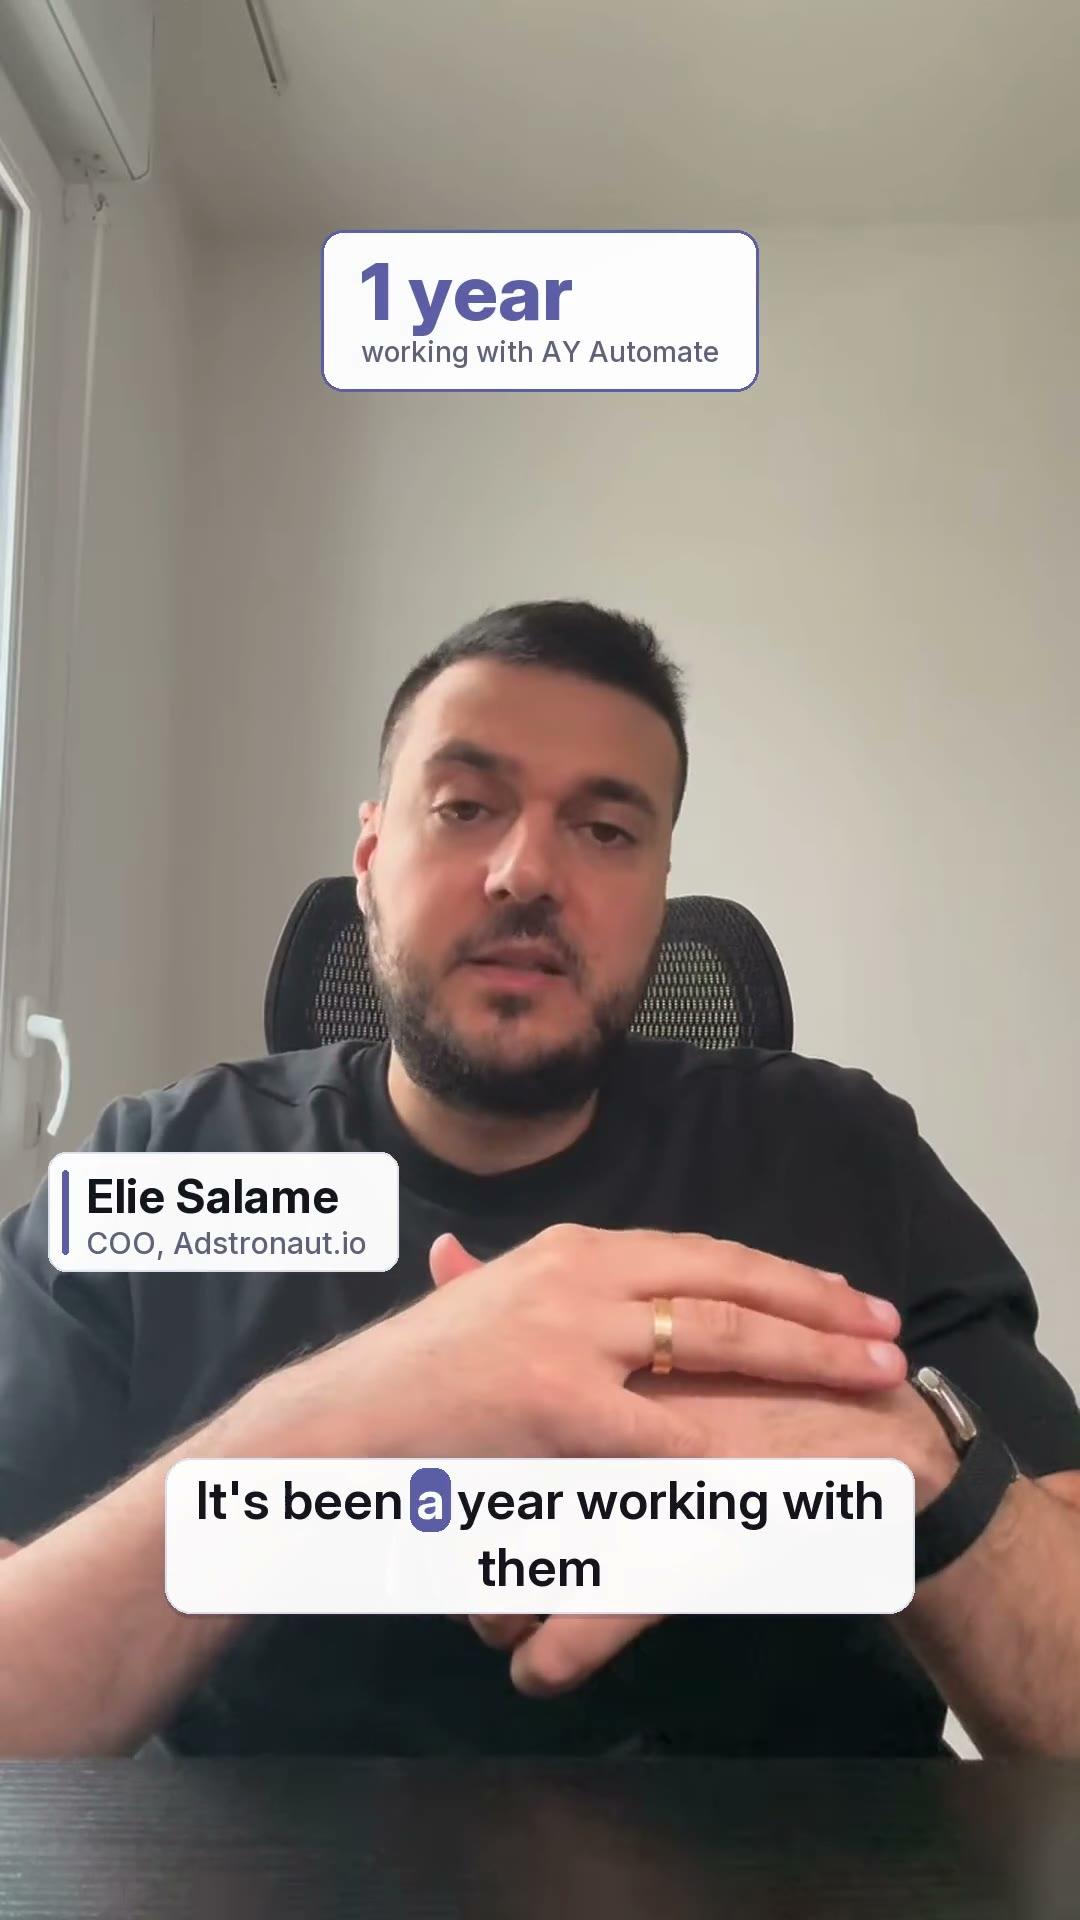
Elie Salame
COO · Adstronaut.io
Elie Salame
COO · Adstronaut.io
Get your AI-written code audited
Send the repo scope and the tools your team uses. We tell you what we check and what a fix pass looks like.
Related
- MCP development
Build MCP servers with trust boundaries.
- Enterprise MCP implementation
Governed MCP for larger teams.
- AI governance assessment
Score your AI governance gaps.
Book a free
30-min security review
Tell us how your team is currently using Claude Code or other AI coding tools. We will name your top exposure points and outline what a full hardening engagement would cover.
Claude Code Security: FAQ
What does an AI code security audit cover?+
We review code and configuration produced with AI coding tools such as Claude Code, Copilot and Cursor: exposed secrets, prompt injection paths, MCP server trust, permissive agent settings and dependency risk. You receive a written report and a hardened configuration package.
Do you offer AI-generated code audit services for a codebase that is already live?+
Yes. Send the repo scope and the tools your team used. The free call confirms what we would check and what a fix pass looks like before you commit to anything.
Is Claude Code a security risk for enterprise teams?+
Claude Code is a powerful tool but ships with permissive defaults: it can read any file it can access, execute shell commands, and send your code to Anthropic's API. Without a hardened configuration, sensitive files like .env secrets, private keys, and internal architecture documents can end up in the AI's context window and transmitted externally. With the right setup - .claudeignore, command allowlists, and approval gates - these risks are manageable.
What is prompt injection in AI coding agents?+
Prompt injection is when an attacker embeds hidden instructions inside a file, comment, or README that Claude Code reads. When the agent processes that file, it may execute the attacker's instructions - exfiltrating data, modifying code, or running unauthorized commands - believing them to be legitimate user requests. It is the most critical and underappreciated risk in AI-assisted development.
How do I prevent Claude Code from reading my .env files?+
The most direct fix is adding .env and credential files to your .claudeignore configuration. This explicitly tells Claude Code to skip those files when exploring your codebase. You should also add secrets directories, private key files, and any files containing database connection strings. We configure a properly scoped .claudeignore as part of the hardening engagement.
What is YOLO mode and why is it a security concern?+
YOLO mode (surfaced in the Claude Code source leak as classifyYoloAction()) is an auto-approval mechanism that bypasses human confirmation for tool calls classified as low or medium risk. The problem: that risk classification is based on heuristics, not context. A medium-risk shell command in a dev environment is very different from one running against a production database. We help teams define explicit approval gates that override auto-approval for sensitive operations.
How should we vet MCP servers before adding them to Claude Code?+
MCP (Model Context Protocol) servers extend what Claude Code can do - but a malicious or compromised MCP server can exfiltrate context, execute code, or escalate permissions. Before adding any MCP server you should: verify the source and maintainer, review the server's declared tool definitions, run it in an isolated network environment, and restrict the filesystem and network permissions available to it. We conduct MCP server security reviews as part of our audit.
Does Claude Code send my code to Anthropic's servers?+
Yes. Code, file contents, and terminal output included in the context window are sent to Anthropic's API for inference. This is expected behavior, but it means your intellectual property, internal architecture, and potentially sensitive logic travels over the network. Enterprise teams should configure .claudeignore to exclude proprietary modules, evaluate Anthropic's data handling policies against their compliance requirements, and consider whether on-premise alternatives are needed for the most sensitive workstreams.
What exactly is in scope for the Claude Code audit?+
Our audit reviews: .claudeignore configuration and file access scope, shell command policies and approval gates, MCP server inventory and trust posture, secrets exposure risk in the current workflow, AI-generated code quality and vulnerability patterns, developer practices around context hygiene, and CI/CD integration for automated security scanning of AI-generated output. You receive a written report with prioritized findings and a hardened configuration package.
How long does an AI code security engagement take?+
A focused audit for a team of up to 20 developers typically runs 1-2 weeks from kickoff to final report. Hardening implementation adds 1 week. Training workshops are delivered in a single day. Ongoing monitoring is a retainer that starts after the initial engagement. We can scope a faster 3-day rapid assessment for teams with urgent compliance deadlines.
How is this different from Claude Code's built-in /security-review command or a generic penetration test?+
The built-in /security-review command and its GitHub Action catch code-level issues in a given pull request, things like SQL injection, missing input validation, or an outdated dependency. A generic penetration test targets your application's attack surface: APIs, auth flows, network exposure. Our audit covers a different layer entirely: whether Claude Code itself is configured safely across your team, meaning file access scope, MCP server trust, shell command approval gates, and hook policies. A codebase can pass every pull request review and every pentest and still expose a live prompt injection or credential leak vector through the agent's own configuration. Most teams get the most value running the built-in review on every pull request and our audit on the underlying setup.
How is a Claude Code security audit priced?+
Pricing is scoped to team size and the number of MCP servers and integrations in use, not a fixed rate card. On the free 30-minute call we ask about your current setup and give you a specific quote before any paid work starts, in line with the audit and harden timelines described above.
What are the signs an AI-built app needs a code audit?+
Four common ones: API keys or secrets sit in the repo or get pasted into prompts, nobody on the team can explain parts of the code an agent wrote, AI-assisted pull requests merge without a security scan, and agents run with shell or MCP access that nobody has reviewed. If two of those apply, book the free call and we name the top risks before any paid work.
How can I audit code generated by Claude Code or Copilot for compliance?+
Treat AI-generated code as untrusted input: scan every AI-assisted pull request with SAST in CI, require human review before merge, and keep a record of which agent touched which files. We set up that pipeline, then map the findings to the OWASP Top 10 for Agentic Applications 2026 so your compliance team has a named framework to point to.
How do I record or audit what AI coding agents like Claude Code and Cursor do?+
Log every tool call at the configuration layer. In Claude Code, PreToolUse and PostToolUse hooks can record and block commands before and after they run, and approval gates stop destructive or network-touching actions until a developer confirms. We configure those hooks, add alerting on policy violations, and document how each action traces back to a developer.
What can an AI coding agent touch on a developer machine?+
With default settings, anything the developer account can reach: every readable file including .env and private keys, the shell, the network, and whatever each MCP server exposes. That context can be sent to the model provider with each prompt. The audit maps that access for every developer setup, then the hardening pass cuts it down to what the work actually needs.
Do you audit small teams or only enterprise engineering orgs?+
Both. Pricing is scoped to team size and the number of MCP servers and integrations in use, so a five-person team pays for a smaller scope than a fifty-person one. Tell us how many developers use AI coding tools and which ones on the free call, and you get a specific quote before any paid work starts.
Do we have to stop using Claude Code during the audit?+
No. The audit reads your configuration, hooks, .claudeignore, MCP server inventory and developer practices while your team keeps shipping. Hardening changes are documented and version-controlled, so they roll out like any other config change and can be reviewed before they land. Training is a single day, scheduled around your release calendar.
Who is this audit not for?+
Teams that do not use AI coding agents yet, and teams that only need an application penetration test of their APIs and auth flows. This audit covers how the agent itself is configured and what it can reach. If that is not your risk, a standard pentest or the built-in /security-review command on each pull request is the better fit.
Can you review an AI agent before it goes to production, not just coding tools?+
Yes. We review custom AI coding agents and internally built assistants for the same risks: tool permissions, prompt injection, secrets handling and sandbox isolation. For agents that act on business systems, start with our production readiness checklist, then book the call and we scope which checks your agent needs before launch.